HEINI · Trust you can inspect
Every AI decision remains explainable.
You do not have to believe HEINI. You have to be able to trace his decisions.
Every operational step connects source, rationale, responsible role, time and consequence. HEINI records what was proposed, changed, stopped or approved.
- Hetzner Falkenstein
- Segregated customer area
- DPA
- No model training
- Audit record
Product proof · Trust
Trust means you can explain it later.
HEINI shows which data supports a proposal, who decided and which consequence followed.
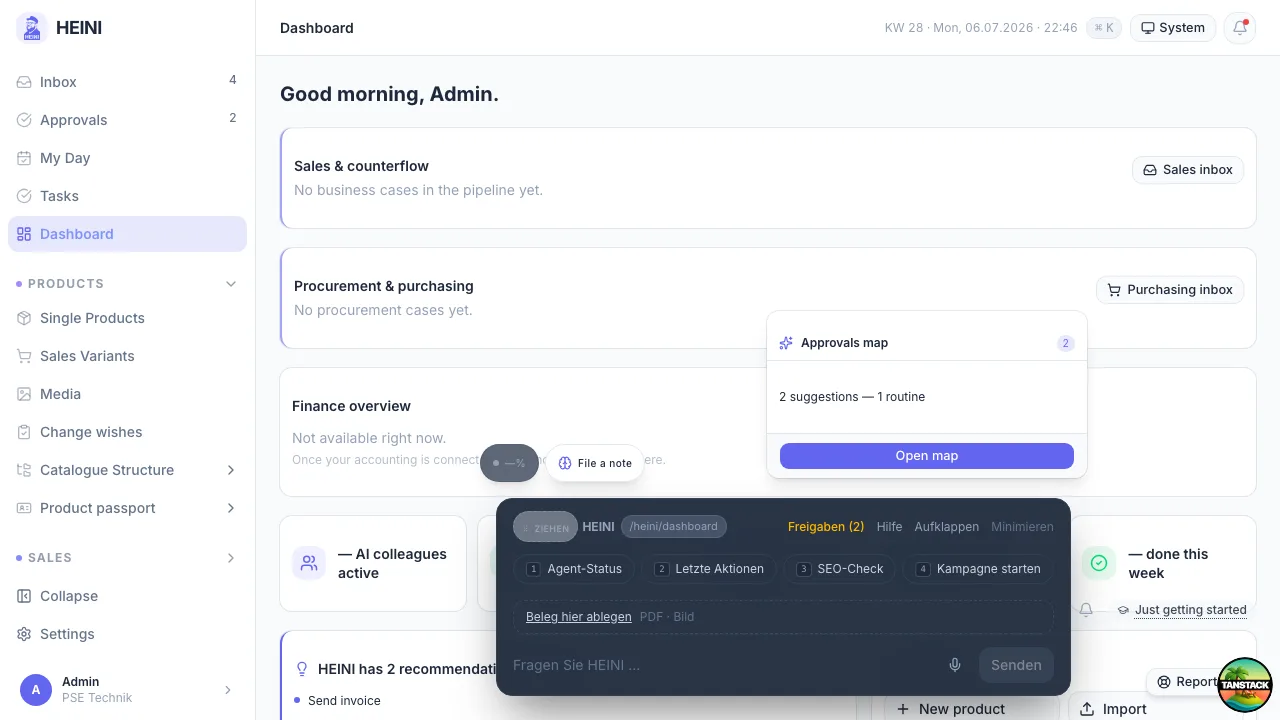
Set delivery date to Friday and prepare the customer reply.
Nothing has been sent or changed yet.
- SourceCarrier confirmation
- RoleSales lead
- Time14 Aug 2026 · 10:42
No customer reply has been sent yet.
Proposal, change, responsibility and consequence are traceable.
Nothing has been sent or changed yet.
What HEINI takes off your desk
Five answers before every productive step
- 01
Which source?
The data, evidence and rules behind a proposal remain visible.
- 02
Why this proposal?
HEINI explains reasons and marks uncertainty in plain language.
- 03
Who is responsible?
Roles, permissions and approval thresholds are checked on the case.
- 04
What happens next?
The operational consequence is visible before approval.
- 05
Who decided when?
Proposal, change and approval enter a traceable record.
How the work moves forward
From proposal to evidenced state
HEINI shows which data supports a proposal, who decided and which consequence followed.
- 01
Connect sources
HEINI shows which data supports the proposal and where information is missing.
- 02
Show risk and consequence
Deviation, affected systems and intended step are disclosed in advance.
- 03
The role decides
Change, stop or approve — within the configured responsibility.
- 04
Record the decision
Who, when, why and with which consequence remain inspectable.
What is already included
Privacy and AI compliance in plain language
01German data location
Standard operations run at Hetzner in Falkenstein. Customer areas are segregated.
02DPA under Art. 28 GDPR
Processing and subprocessors are governed in the data processing agreement.
03No customer data for third-party model training
Operational data is not used to train third-party models.
04Human oversight
HEINI presents irreversible or external consequences to responsible people for a decision.
05Honest certification status
We do not present provider certifications as HEINI product certifications or claim evidence we do not have.
Hosting
Standard hosting is at Hetzner in Falkenstein. Provider certifications refer to their stated scope; they are not HEINI product certification.
Privacy and processing agreements
Website enquiries and customer processing have different responsibilities. Read the applicable terms:
Privacy notice · DPAGoBD preparation
Sources, changes and approvals support traceability. Compliance also depends on your procedures and actual operation; the software alone does not establish it.
Trust · human decision
Prepared means traceable — not decided.
HEINI shows sources, open questions and consequences. Only your go-ahead changes the operational state. Every decision is recorded with role, time and rationale.
The product and contractual state is authoritative. Provider certifications are not HEINI product certifications.
- GDPR
- EU AI Act
- GoBD preparation
- Exit & deletion
- Before approval
- No customer reply has been sent yet.
- Record
- Proposal, change, responsibility and consequence are traceable.
FAQ
Facts for IT and privacy teams
Where is operational data stored?
In standard operation, in a segregated customer area at Hetzner Falkenstein, Germany. Details and possible subprocessors are documented in the DPA.
Do model providers train on our data?
Customer data is not used to train third-party models. Processing for model inference is contractually and technically constrained.
Is HEINI ISO or C5 certified?
We claim no HEINI product certification without the corresponding evidence. Hosting-provider certifications are named as such.
How does HEINI support AI compliance?
Through visible sources, roles, human approvals and a traceable decision record. The specific legal assessment remains with the responsible organisation.
Your business. Your case.
Review HEINI with your IT and privacy team.
We walk through architecture, DPA, approval path and record on a real case.
See HEINI on your own case